With remote and hybrid work, users follow an “anywhere-anytime” culture and switch between personal laptops, tablets, and phones to get their work done. This flexibility reduces costs and improves productivity, but it also brings serious security risks.
One risk that often looks harmless but can cause real damage is unmanaged devices. They sit outside your IT team’s security controls, so when users access Microsoft 365 from them on an insecure network, your organization can lose sensitive business data.
So, let’s explore what unmanaged devices are in Microsoft Entra ID, how they put businesses at risk, and how to block unmanaged devices, limit their access, and monitor their sign-ins.
What are Unmanaged Devices in Microsoft 365?
Unmanaged devices are devices that are not actively managed and monitored by your IT department.
In Microsoft Entra ID, a device counts as managed when it is Microsoft Entra hybrid joined or enrolled in Microsoft Intune (or another supported MDM). Conditional Access can go one step further and require the device to be marked as compliant with Intune compliance policies.
- A device that meets none of these, such as a personal laptop, a home PC, or a personal phone used for work (BYOD), is unmanaged.
- This also includes devices that are only Microsoft Entra registered, such as a personal phone where the user has added a work account. Entra ID knows about these devices, but your organization doesn’t manage them.
Unmanaged doesn’t mean unwelcome, though. Businesses generally benefit from letting employees work from anywhere on any device, as long as the right safety measures are in place. But when unmanaged (BYOD) devices are not fully understood, they can become a security risk to business systems.
For this reason, it’s better to either limit device access or monitor access from unmanaged devices. Below are a few ways to reduce the business risks of unmanaged devices in Microsoft 365.
How to Block or Limit Unmanaged Devices in Microsoft 365
BYOD (Bring Your Own Device) approaches carry a higher risk of complications, so it’s essential to address all privacy and security issues first. That’s why it’s a good idea to block unmanaged devices from accessing your cloud apps.
A Conditional Access policy for unmanaged devices is the most effective way to do this. It checks the device’s state at every sign-in and allows access only from devices your organization manages.
Depending on how strict you need to be, you can block or limit unmanaged devices in these ways:
- Block all Microsoft 365 apps: Block unmanaged devices using Conditional Access
- Allow browser-only access to files: Limit SharePoint and OneDrive access
- Make email read-only in the browser: Block attachment downloads in Outlook on the web
- Protect work apps on personal phones: Use Intune app protection
- Cut off risky sessions faster: Use CAE and token protection
Before you set up any of these, make sure your tenant has the required licences:
- Conditional Access requires Microsoft Entra ID P1, which is included in Microsoft 365 E3, E5 and Business Premium.
- Requiring a compliant device also requires the device to be enrolled in Intune.
- Without P1, security defaults still give you baseline protection, but they can’t check whether a device is managed.
1. Block Unmanaged Devices Using Conditional Access Policy
Follow these steps to create a Conditional Access policy that allows access to Microsoft 365 apps only from managed devices.
- Sign in to the Microsoft Entra admin center with at least the Conditional Access Administrator role.
- Go to Entra ID → Conditional Access → Policies and click + New policy.
- Enter a name for the policy, for example, Require managed device for Microsoft 365.
- Under Users, include All users or a pilot group. On the Exclude tab, exclude your break-glass accounts so that you can’t lock yourself out.
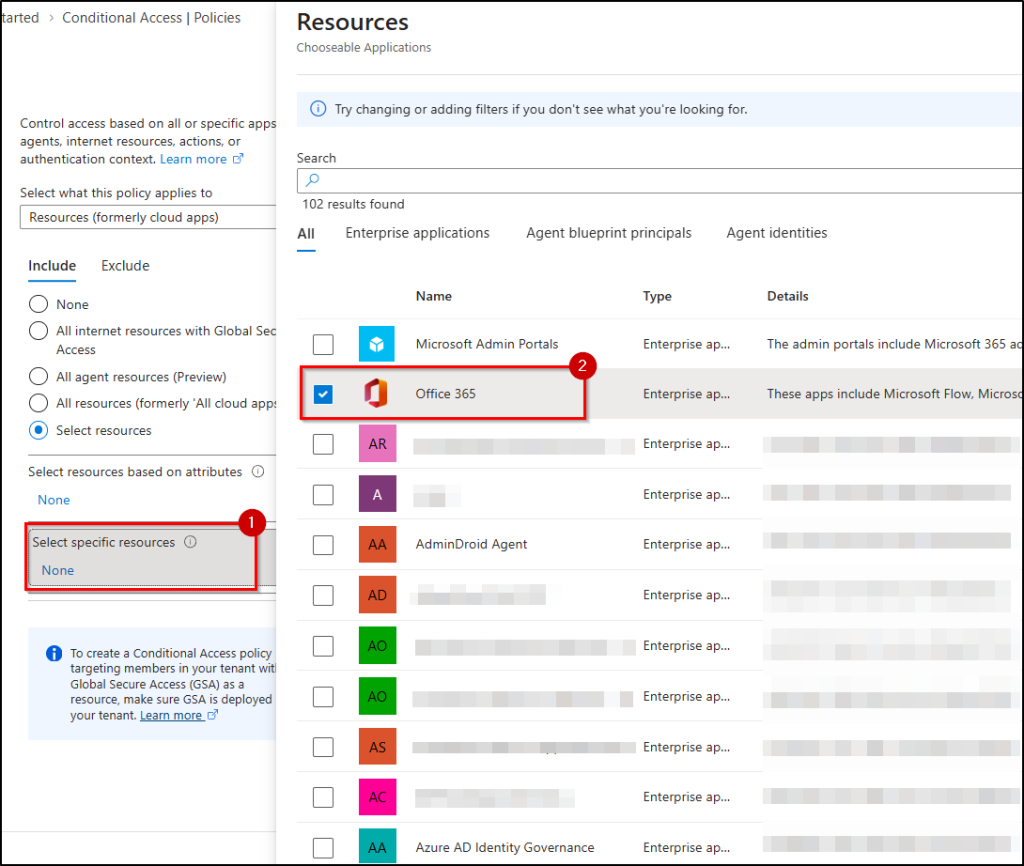
- Under Target resources, choose Select resources and pick Office 365. This covers Exchange Online, SharePoint Online, OneDrive, Microsoft Teams, and the other Office 365 apps.
6. Under Grant, select Grant access, check Require device to be marked as compliant and Require Microsoft Entra hybrid joined device, and choose Require one of the selected controls.
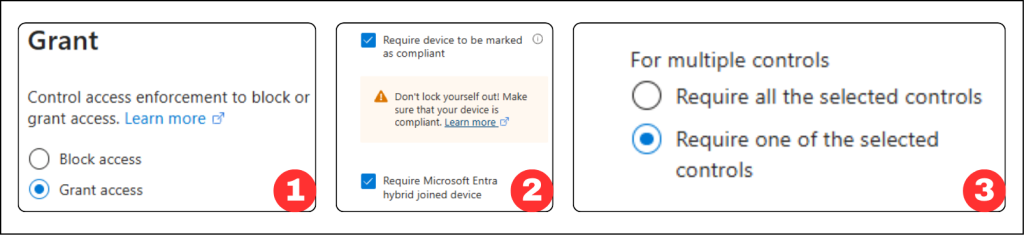
7. Set Enable policy to Report-only and click Create. Then switch the policy On when required.
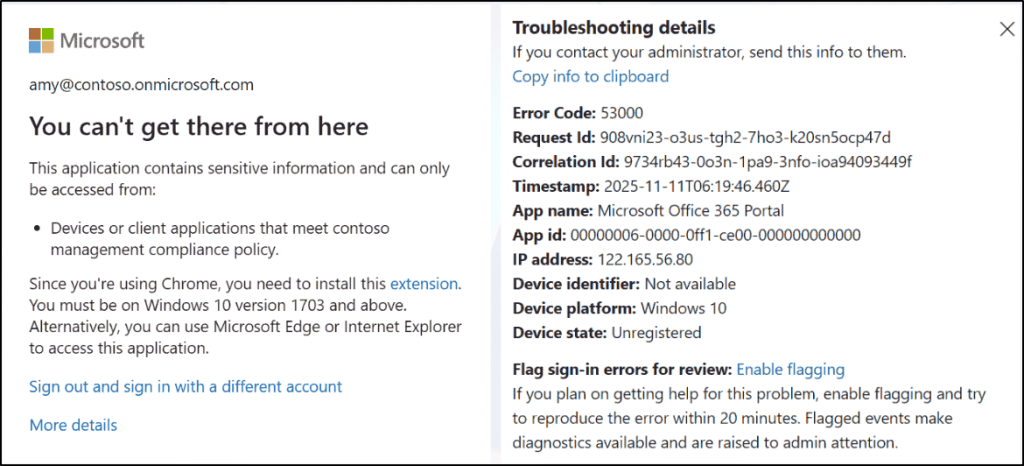
Once the policy is on, users who sign in from an unmanaged device are blocked from Microsoft 365 apps. The sign-in log records error code 53000 – Device is not in required device state.
You can’t get there from here. This application contains sensitive information and can only be accessed from:
Devices or client applications that meet <tenantname> management compliance policy.
2. Set Up Access Limits to SharePoint and OneDrive Files
A full block suits high-security environments, but not every organization can afford to shut out unmanaged devices completely! Some users still need access to certain apps from anywhere for instant communication. When that happens, you can limit access instead of blocking it.
Among Microsoft 365 apps, SharePoint and OneDrive store most of your organization’s confidential files. So, it is important to limit access to SharePoint and OneDrive content from unmanaged devices.
For example, say your organization wants users to keep access to all services on unmanaged devices, but with only browser-based access to SharePoint and OneDrive. To set this up:
- Open the SharePoint admin center, go to Policies → Access control.
- Select Unmanaged devices.
- Choose Allow limited, web-only access and click Save.
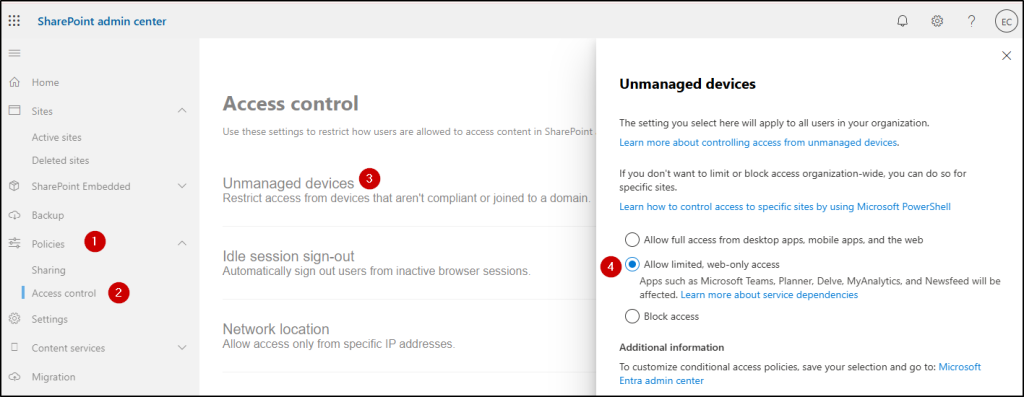
Limiting user access reduces the risk of accidental data loss on unmanaged devices. With this setup, users on unmanaged devices get browser-only access: they can view files but can’t download, print, or sync them.
Users then see a message like this when they open SharePoint:
Your organization doesn’t allow you to download, print, or sync using this device. To use other actions, use a device that’s joined to a domain or marked compliant by Intune. For help, contact your IT department.
Saving this setting automatically creates two Conditional Access policies in Microsoft Entra ID. Their names start with [SharePoint admin center]: Use app-enforced restrictions for browser access, and the other [SharePoint admin center]: Block access from apps on unmanaged devices.
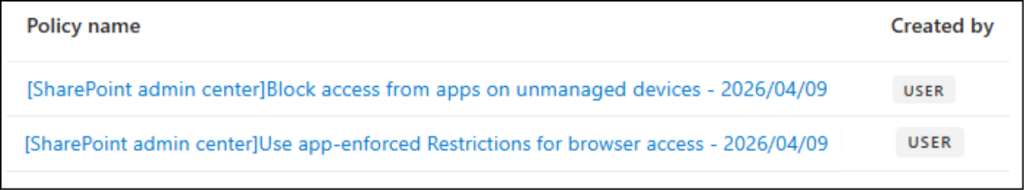
Tip: If only a few sensitive sites, such as Finance or HR, need these limits, you can restrict unmanaged device access for specific SharePoint sites using PowerShell or sensitivity labels instead of applying them tenant-wide.
3. Block Attachment Downloads in Outlook on the Web from Unmanaged Devices
SharePoint isn’t the only place where company data reaches unmanaged devices. Emails and attachments can just as easily be saved to them. As with SharePoint, you can make Outlook on the web read-only on unmanaged devices.
- Connect to Exchange Online PowerShell and run the cmdlet below. It updates the default Outlook on the web mailbox policy, which applies to all users unless you’ve assigned them a custom policy.
|
1 |
Set-OwaMailboxPolicy -Identity "OwaMailboxPolicy-Default" -ConditionalAccessPolicy ReadOnly |
You can use either of these values for the ConditionalAccessPolicy parameter:
- ReadOnly: users can view but not download attachments in the default policy.
- ReadOnlyPlusAttachmentsBlocked: users can’t view or download attachments at all.
2. Next, create a Conditional Access policy in the Entra admin center, following the same steps as above, but change these settings:
- Target resources: Office 365 Exchange Online
- Session: Use app-enforced restrictions
If you’ve excluded Exchange Online from your block policy so these users can use read-only Outlook on the web, exclude the OwaDownloadAttachments app as well. Outlook on the web and the new Outlook now handle attachments through this separate app, which Conditional Access evaluates on its own. Without the exclusion, users can still read their mail but can’t view, download, or upload attachments at all. It’s worth reviewing how Conditional Access applies to Outlook attachments before you rely on such exclusions.
4. Protect Data on Personal Phones with Intune App Protection
Outlook on the web limits cover browsers, but most users read work email in mobile apps on their personal phones. Blocking every personal phone would cut users off from email on the go.
Instead, Intune app protection policies (MAM) protect company data inside apps such as Outlook, Teams, and OneDrive without enrolling the device. You can create them in the Microsoft Intune admin center → Apps → App protection policies to do the following:
- stop users from copying company data into personal apps
- require a PIN to open work apps
- wipe only company data if the phone is lost
To enforce them, pair app protection policies with Conditional Access using the Require app protection policy grant for iOS and Android.
5. Strengthen Sessions with CAE and Token Protection
Conditional Access, SharePoint limits, and app protection are all checked when a user signs in. But a session can stay active after the risk changes, for example when an account is disabled or a token is stolen. Two more controls close that gap:
- Continuous Access Evaluation (CAE) lets Exchange Online, SharePoint Online and Teams revoke access within minutes of a critical event, such as a user being disabled or their password being reset, instead of waiting for the access token to expire.
- It’s turned on by default, but it’s worth knowing how continuous access evaluation works so that you can confirm none of your Conditional Access policies disable it.
- Token protection is a Conditional Access session control that accepts only sign-in tokens bound to the device they were issued to. So, even if a token is stolen, it can’t be replayed from another machine, which makes it one of the strongest defenses against OAuth phishing attacks like ConsentFix.
- You can enforce token protection with a Conditional Access policy for Exchange Online, SharePoint Online, and Teams in desktop and mobile apps.
How to Monitor Unmanaged Devices in Sign-in Logs?
All these controls reduce risk, but they don’t remove it. Security threats remain the biggest concern with unmanaged devices in Microsoft 365.
For instance, imagine a user who needs to communicate right away. If you block every unmanaged device, how will they communicate? That creates a communication gap. So, blocking all unmanaged devices won’t work in every case.
We can’t avoid unmanaged devices completely, but we can keep watch on how they’re used. Microsoft 365 records device details for every sign-in in the Microsoft Entra sign-in logs. To review sign-ins from unmanaged devices:
- Open the Microsoft Entra admin center.
- Go to Entra ID → Monitoring & health → Sign-in logs.
- Select Add filters, choose Conditional Access, and set it to Failure. This lists sign-ins that were blocked by a Conditional Access policy. If a sign-in was blocked by your device policy, its Basic info tab shows sign-in error code 53000.
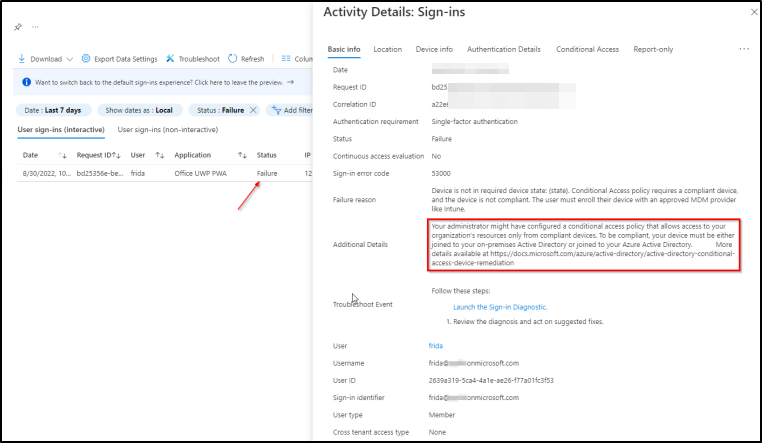
4. Open a sign-in and check the Device info tab.
- The Managed, Compliant, and Join type fields show whether the device was managed.
- The Conditional Access tab shows which policy applied and its result.
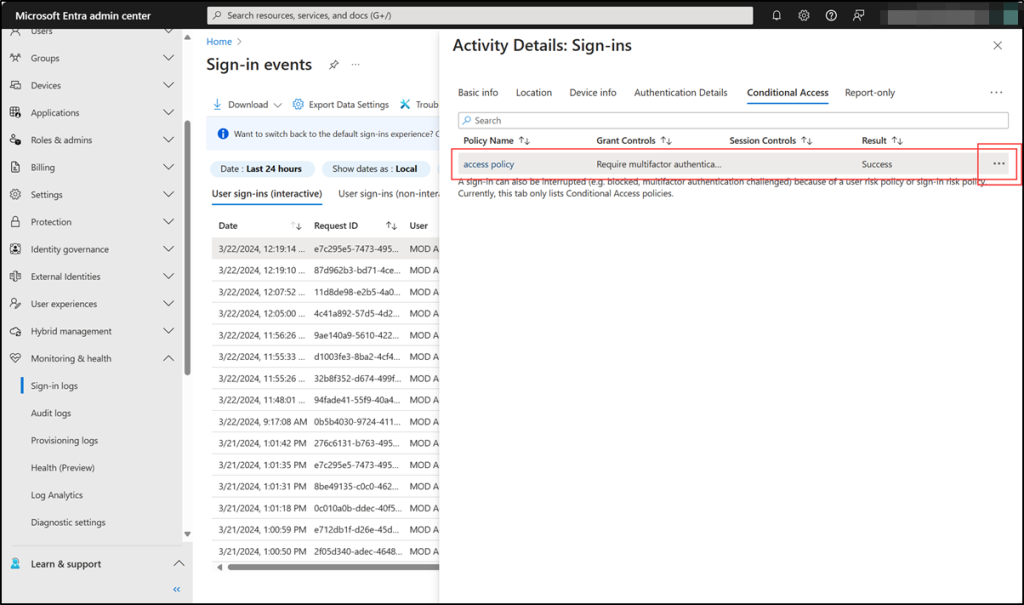
Keep in mind that a failed sign-in is not the same as an unmanaged one. Users who get limited, web-only access sign in successfully, so also review successful sign-ins where Managed is No.
Doing this by hand takes time! The sign-in logs show every sign-in in one long list, with no filter or built-in report for unmanaged devices, so we have to open each sign-in one by one. As a result, risky activity from unmanaged devices can easily go unnoticed.
Never Miss an Unmanaged Device Sign-in with AdminDroid
So, is there a way to see unmanaged device sign-ins directly, without opening every log entry?
Yes! Look no further than AdminDroid, a Microsoft 365 management tool. Its sign-in analytics reports go beyond the limits of native Entra reports, and for unmanaged devices, it offers powerful dedicated reports that do the filtering for you!
The unmanaged device sign-ins report lists every sign-in from devices your organization doesn’t manage, along with device details such as the operating system, browser, and device name. It also separates successful and failed sign-ins, so you can quickly see who is accessing Microsoft 365 from personal devices and which of those attempts your policies blocked.
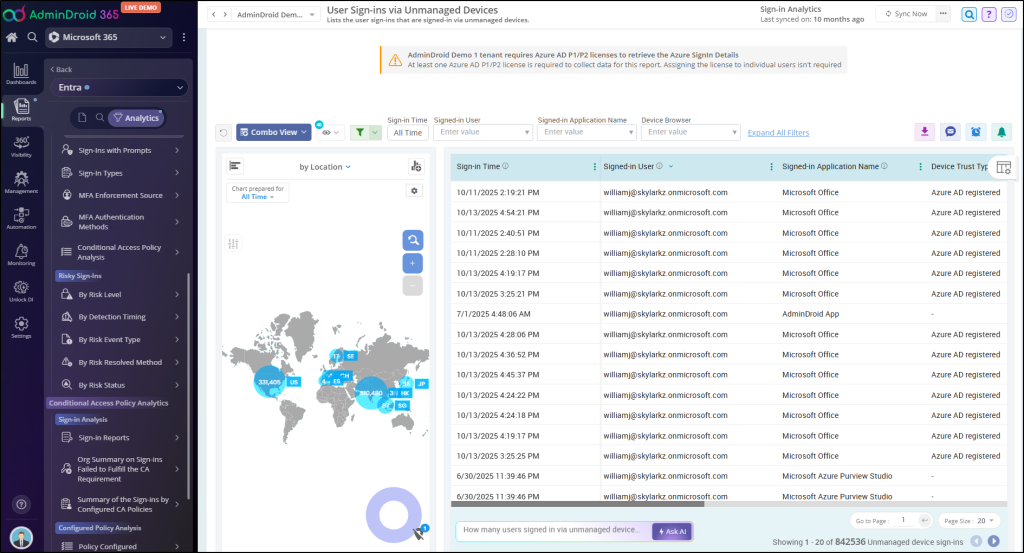
The non-compliant device sign-ins report tracks sign-ins from devices that are known to your organization but don’t meet your compliance policies. Since you already manage these devices, a sign-in from one often points to an outdated OS, missing encryption, or another setting you can fix on the device itself.
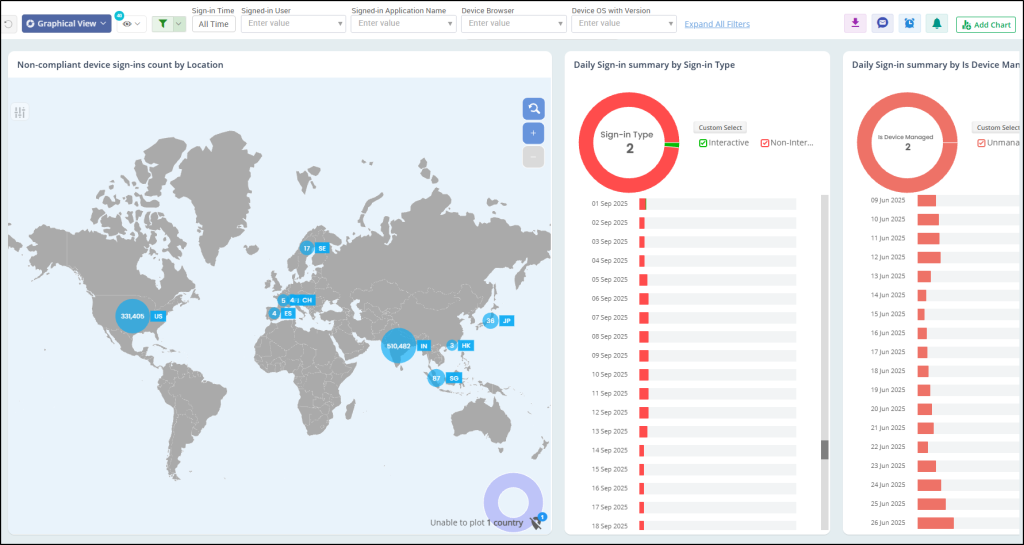
That’s not where we stop! To act on these sign-ins swiftly as they happen, you can set alerts that notify you when users sign in from unmanaged or non-compliant devices.
Together, these reports and alerts help you monitor risky sign-in attempts from unmanaged devices without digging through the Entra sign-in logs one entry at a time!
Explore AdminDroid’s features with a free trial now!