Over the past few years, Microsoft has warned admins about the deprecation of Basic Authentication in Exchange Online. Since it’s one of the oldest authentication methods, it comes with numerous security flaws. Hackers can easily attack accounts that use basic auth, as it requires only a username and a password to log in. Therefore, Microsoft decided to deprecate basic authentication in Exchange Online.
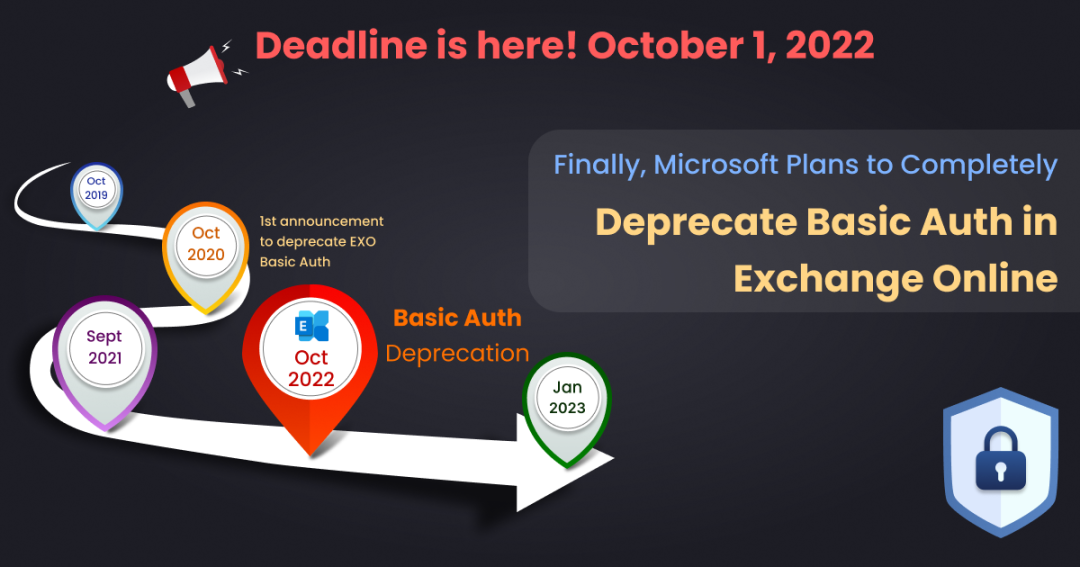
Due to the pandemic, Microsoft postponed the deprecation several times. But it finally happened!
Microsoft began disabling basic authentication in Exchange Online on October 1, 2022. By early 2023, it was turned off in all tenants, including those that had requested a temporary re-enablement.
But it’s not over yet! SMTP AUTH was left as the only exception, and Microsoft is now retiring basic auth for it too. Exchange Web Services (EWS) itself is also being retired in Exchange Online. So, if your organization still has apps, scripts, or devices that rely on basic auth or EWS, now is the time to act.
Which Exchange Online Protocols Still Support Basic Authentication?
Here’s where each protocol stands today:
| Protocol | Basic auth status | Can you re-enable it? |
| Exchange ActiveSync, POP, IMAP, Remote PowerShell, Offline Address Book, Autodiscover, Outlook for Windows and Mac | Permanently disabled | No. The option ended on December 31, 2022. |
| SMTP AUTH (Client Submission) | Still available. It will be disabled by default for existing tenants at the end of December 2026. | Yes, until the final removal date, which Microsoft will announce in the second half of 2027. |
| Exchange Web Services (EWS) | Basic auth is disabled, and EWS itself is being retired. Phased disablement started on October 1, 2026. | Only for allowed apps, until EWS is permanently disabled on April 1, 2027. |
Any app, script, or device that still uses a username and password through these protocols will fail to connect. The deprecation also stops app passwords from working with apps that don’t support two-step verification.
Is SMTP AUTH Basic Authentication Also Being Deprecated?
Yes. SMTP AUTH was left as an exception because many printers and scanners can’t use modern authentication.
- Microsoft announced its retirement on April 15, 2024, and revised the timeline on January 27, 2026.
- Tenants created after December 2026 won’t have SMTP AUTH basic auth by default.
Once it’s permanently removed, devices that still use it will receive the error “550 5.7.30 Basic authentication is not supported for Client Submission.”
550 5.7.30 Basic authentication is not supported for Client Submission.
So, identify the printers, scanners, apps, and workflows that still use SMTP AUTH basic auth, and move them to OAuth or another supported sending method before the end of December 2026.
Can You Still Re-enable Basic Authentication?
It depends on the protocol. For EAS, POP, IMAP, Remote PowerShell, EWS, OAB, Autodiscover, and Outlook: No.
The temporary re-enablement option ended on December 31, 2022. Now, neither you nor Microsoft Support can turn it back on. If an app stops connecting, find the protocol it uses and move it to modern authentication.
For SMTP AUTH: Yes, for now.
SMTP AUTH is the only protocol that still supports basic authentication. Even after it’s disabled by default at the end of December 2026, admins can turn it back on until Microsoft’s final removal date. So, treat it as a temporary fallback, not a long-term solution.
| IMPORTANT: If security defaults are enabled in your tenant, basic authentication is blocked, and SMTP AUTH is already disabled in Exchange Online. To use SMTP AUTH, you’ll need to turn off security defaults first. |
How to Deal with Exchange Online Basic Authentication Deprecation
The only way forward is to move every app, script, and device from basic authentication to modern authentication. Modern authentication uses OAuth 2.0 tokens that expire and are tied to a specific app, so they can’t be reused like a stored password. It also makes it simple to enforce MFA and Conditional Access.
Follow these four steps:
- Step 1: Identify basic authentication usage using the Entra sign-in logs
- Step 2: Move apps and scripts to modern authentication
- Step 3: Disable basic authentication in Exchange Online
Step 1: Identify Basic Authentication Usage in Entra Sign-in Logs:
Before you disable anything, find out who and what still uses basic authentication. The following reports help you identify them:
Export the Basic Authentication Report from Microsoft Entra Sign-in Logs
To find users and apps signing in with legacy authentication in Microsoft 365, use the Entra sign-in logs:
1. In the Microsoft Entra admin center, go to Entra ID → Monitoring & health → Sign-in logs.
2. Select ‘Manage view → Edit columns’ and add the column Client app to add the Client app column, since it isn’t shown by default. This column shows the protocol used for each sign-in.
3. Select Add filters → Client app, and choose all Legacy Authentication Clients, such as Authenticated SMTP, Exchange ActiveSync, Exchange Web Services, IMAP4, POP3, and Other clients. Skip Browser and Mobile Apps and Desktop Clients, as they use modern auth.
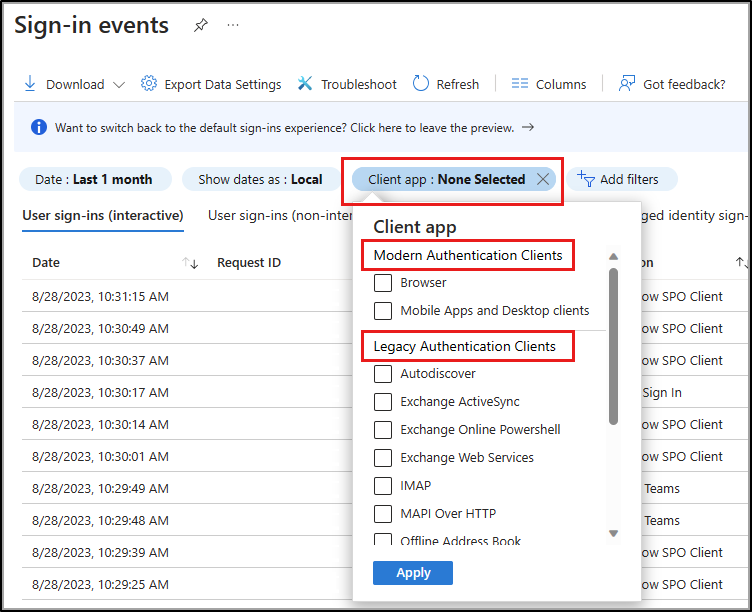
4. Repeat the same steps on the User sign-ins (non-interactive) tab. Non-interactive logs capture background sign-ins from apps and automated workflows that the interactive tab misses.
5. The filtered list now shows the users and apps signing in with basic authentication. Select any entry to see its client app, resource, status, and IP address, and select Download to export the report as a CSV or JSON file.
Note: he logs show only sign-ins within the selected period, so check with app owners for rarely used scripts and devices.
Find SMTP AUTH Basic Auth Usage Using the Exchange Admin Center
Go to Exchange admin center → Reports → Mail flow → SMTP AUTH clients report.
- In the Messages sent using SMTP Auth section, the Authentication Protocol column shows whether each sender uses Basic Auth or Modern Auth.
- The report also shows TLS usage and message volume, and you can export it as a CSV file. Set the date range to the maximum of 90 days to catch devices that send email only occasionally.
Find Apps That Use EWS Using the Microsoft 365 Admin Center
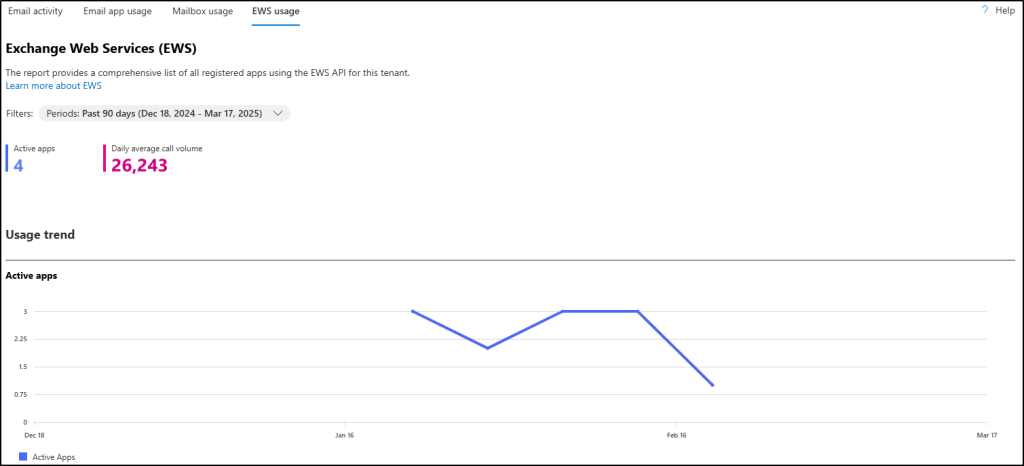
Go to Microsoft 365 admin center → Reports → Usage → Exchange, and select the EWS usage tab.
Below the usage trend, the Usage details table lists each app’s Application ID, the EWS operations it calls (SOAP actions), call volume, and last activity date. Use these application IDs to plan the app’s move to Microsoft Graph or to allow it temporarily.
Step 2: Move Apps and Scripts to Modern Authentication
Once you know what still uses basic auth, move each app, script, and device to modern authentication. Jump to the protocol you need:
- Migrate POP, IMAP, and SMTP AUTH Apps to OAuth 2.0
- Connect to Exchange Online PowerShell Using the EXO V3 Module
- Move Exchange ActiveSync Devices to Modern Authentication
- Migrate Exchange Web Services (EWS) Apps to Microsoft Graph
- Upgrade Outlook Clients That Don’t Support Modern Authentication
Migrate POP, IMAP, and SMTP AUTH Apps to OAuth 2.0
Apps can keep using POP, IMAP, and SMTP AUTH, but they must sign in with OAuth 2.0. For email clients like Thunderbird, update the app and switch the account to OAuth. Outlook isn’t affected, as it uses its own protocols to connect to Exchange Online.
For in-house apps, implement OAuth. If the app runs in the background without a signed-in user, it can’t sign in as a user, so it needs its own identity in Microsoft Entra ID. Set this up using the client credentials flow:
- In the Microsoft Entra admin center, go to Entra ID → App registrations and register the app. This gives it an Application ID.
- Open the app, select Certificates & secrets, and add a client secret or certificate for the app to sign in with.
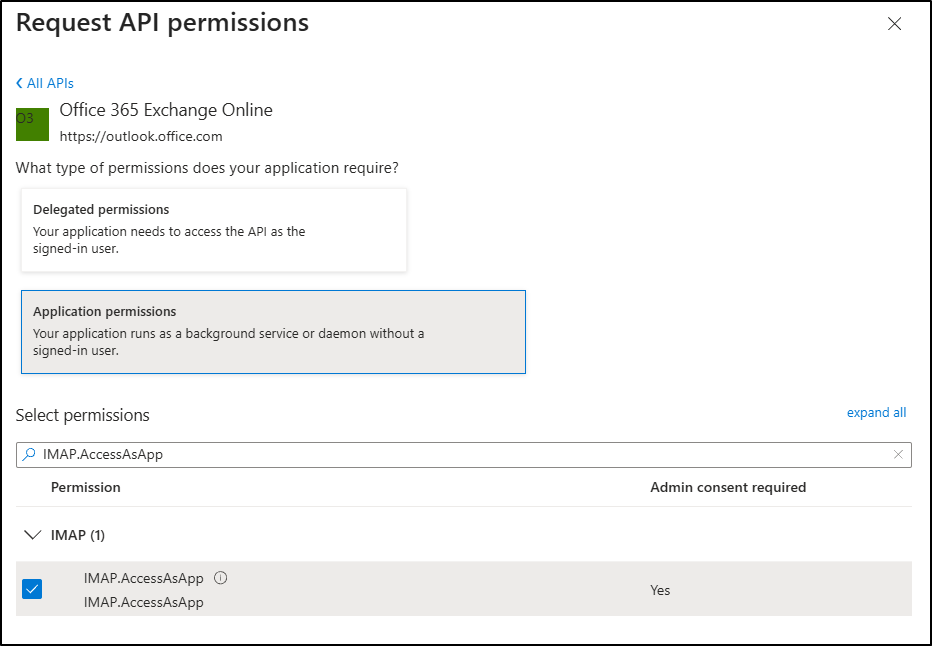
- Select API permissions under Manage. Then, select Add a permission → APIs my organization uses, search for Office 365 Exchange Online, and select Application permissions.
- Select POP.AccessAsApp, IMAP.AccessAsApp, or SMTP.SendAsApp as required, and then select Add permissions. Finally, select Grant admin consent for <your organization>.
3. Register the app’s service principal in Exchange Online, and grant it access only to the mailboxes it needs:
|
1 2 |
New-ServicePrincipal -AppId <ApplicationId> -ObjectId <EnterpriseAppObjectId> Add-MailboxPermission -Identity <MailboxUPN> -User <ServicePrincipalId> -AccessRights FullAccess |
Note: Use the Object ID from Enterprise applications, not App registrations. A wrong Object ID causes authentication to fail.
Connect to Exchange Online PowerShell Using the EXO V3 Module
Since October 2023, REST API connections have replaced Remote PowerShell in Exchange Online and Security & Compliance PowerShell. The EXO V3 module uses modern authentication and doesn’t need WinRM basic auth. Install or update it, and then connect:
|
1 2 3 |
Install-Module -Name ExchangeOnlineManagement Update-Module -Name ExchangeOnlineManagement Connect-ExchangeOnline -UserPrincipalName <upn> |
Note: If you use PowerShell 7, the latest module versions require PowerShell 7.6 or later. Windows PowerShell 5.1 isn’t affected.
For unattended scripts, use certificate-based app-only authentication instead of stored passwords. If you enabled WinRM basic auth for older modules, turn it off. In Command Prompt (as administrator), check the setting, and if it shows Basic = true, disable it:
|
1 2 |
winrm get winrm/config/client/auth winrm set winrm/config/client/auth @{Basic="false"} |
Move Exchange ActiveSync Devices to Modern Authentication
Mobile devices using basic auth can no longer sync email. So, users can switch to:
- Outlook for iOS and Android, which supports Conditional Access and Intune app protection.
- Another option is any mail app that supports modern authentication, such as the iOS Mail app (11.3.1 or later).
If an updated app still uses basic auth, remove the account and add it back. For devices managed with Microsoft Intune, update the email profile to use modern authentication.
Migrate Exchange Web Services (EWS) Apps to Microsoft Graph
Microsoft is retiring EWS in Exchange Online, so apps can’t keep using it, even with modern authentication.
- Since October 1, 2026, Microsoft has been switching off EWS in tenants where admins haven’t explicitly allowed it.
- On April 1, 2027, EWS will be permanently disabled, with no extensions. On-premises Exchange Server isn’t affected.
What to do:
- Find the apps: Check the EWS usage report for apps that still call EWS.
- Migrate them: Move apps that access mailbox, calendar, or contact data to Microsoft Graph, and ask vendors for Graph-based versions.
- Keep critical apps running until then: Allow only their application IDs so they keep working until April 2027.
Upgrade Outlook Clients That Don’t Support Modern Authentication
Here are the Outlook versions that support and don’t support modern authentication. If your Outlook version doesn’t support it, upgrade to a newer version.
| Outlook Version | Supports Modern Authentication? |
| Outlook 2007 and 2010 | No |
| Outlook 2013 | Yes (requires registry setting) |
| Outlook 2016 and later (Windows and Mac) New Outlook for Windows | Yes (By default) |
Note: For Outlook 2013, set the DWORD values EnableADAL = 1 and Version = 1 under HKEY_CURRENT_USER\Software\Microsoft\Office\15.0\Common\Identity. However, Outlook 2013 and Office 2016/2019 are out of support, so move to Microsoft 365 Apps or the new Outlook for Windows.
Step 3: Disable Basic Authentication in Exchange Online
With your apps and devices now on modern authentication, nothing in your organization should still need basic auth. Microsoft has already removed it for most protocols, but SMTP AUTH still supports it until its final removal. So, close any basic auth entry points that are still open, and turn off the legacy protocols your users don’t need, to leave attackers fewer ways in. Here’s how to do it:
- Block Basic Authentication Using the Admin Center and PowerShell
- Disable SMTP AUTH, POP, IMAP, and ActiveSync
- Disable Exchange Web Services (EWS)
- Block Legacy Authentication Using Conditional Access
Block Basic Authentication Using the Microsoft 365 Admin Center and PowerShell
Start in the Microsoft 365 admin center to block SMTP basic auth, and then use PowerShell to block the settings it doesn’t show. Both methods work through Exchange Online authentication policies.
1. Turn Off Basic Auth in the Microsoft 365 Admin Center
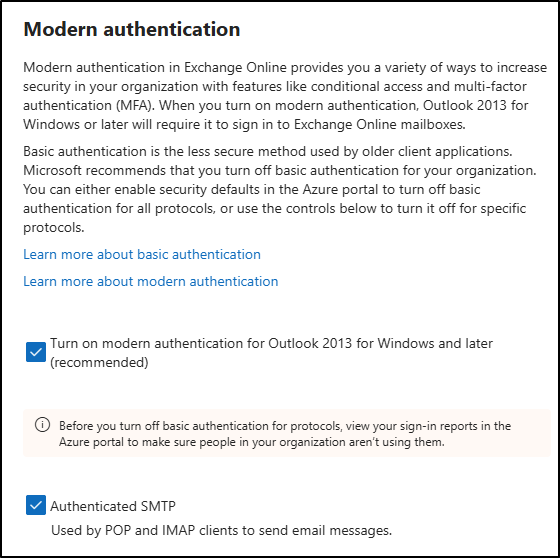
Go to Microsoft 365 admin center → Settings → Org settings → Services → Modern authentication. In the flyout,
- Select Turn on modern authentication for Outlook 2013 for Windows and later (recommended). You can block basic auth only when modern authentication is on, as clients need it to keep signing in.
- Clear the Authenticated SMTP checkbox to block basic auth for SMTP AUTH, and select Save.
SMTP AUTH is the only protocol listed because Microsoft has already removed basic auth for the others. Behind the scenes, this setting creates or updates your organization’s default authentication policy, which you can view only through PowerShell.
2. Block the Remaining Basic Auth Settings Using PowerShell
The admin center doesn’t turn off AllowBasicAuthOutlookService (used by the Mail and Calendar app for Windows 10) or AllowBasicAuthReportingWebServices (used to retrieve report data). Use Exchange Online PowerShell to review and configure these settings.
1. Check existing policies and the organization default:
|
1 2 |
Get-AuthenticationPolicy | Format-List Name, AllowBasicAuth* Get-OrganizationConfig | Format-Table DefaultAuthenticationPolicy |
2. Create and configure a policy to block all basic auth by default:
|
1 2 |
New-AuthenticationPolicy -Name "Block Basic Auth" Set-OrganizationConfig -DefaultAuthenticationPolicy "Block Basic Auth" |
3. Block basic auth for Outlook Service, Reporting Web Services, and SMTP:
|
1 |
Set-AuthenticationPolicy -Identity "<PolicyName>" -AllowBasicAuthOutlookService:$false -AllowBasicAuthReportingWebServices:$false -AllowBasicAuthSmtp:$false |
4. Apply the policy to existing user mailboxes:
The organization default doesn’t automatically replace a policy already assigned to an existing user. To assign this policy to all user mailboxes:
|
1 |
Get-Mailbox -RecipientTypeDetails UserMailbox -ResultSize Unlimited | foreach {Set-User -Identity $_.ExchangeObjectId.ToString() -AuthenticationPolicy "<PolicyName>"} |
The policy takes effect within 24 hours. If a device still needs SMTP AUTH basic auth until you replace it, allow it in a separate policy assigned only to that device’s account.
Disable SMTP AUTH, POP, IMAP, and ActiveSync for Users
Authentication policies block basic authentication, but protocols like SMTP AUTH, POP, IMAP, and Exchange ActiveSync may remain enabled. For added security, disable the ones your organization doesn’t need, and allow them only for the mailboxes that need them.
1. Disable SMTP AUTH in Exchange Online (Organization-wide):
Go to Exchange admin center → Settings → Mail flow and select Turn off SMTP AUTH protocol for your organization.
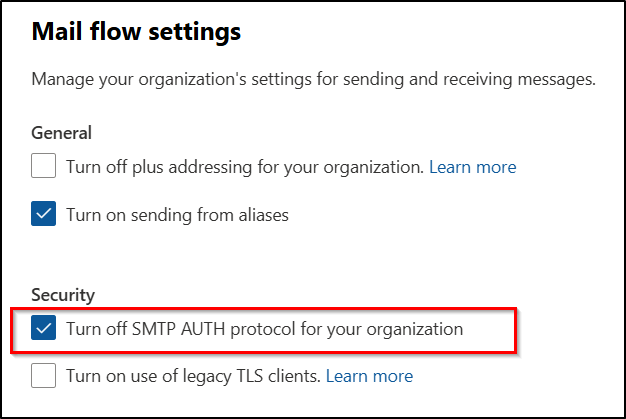
Or run the command below, and confirm the result shows True:
|
1 2 |
Set-TransportConfig -SmtpClientAuthenticationDisabled $true Get-TransportConfig | Format-List SmtpClientAuthenticationDisabled |
If a mailbox, such as a printer’s account, still needs it, enable it for that mailbox only. This mailbox setting overrides the organization setting:
|
1 |
Set-CASMailbox -Identity <MailboxUPN> -SmtpClientAuthenticationDisabled $false |
Note: SMTP AUTH is already blocked if security defaults are enabled. If your authentication policy blocks SMTP basic auth, mailboxes with SMTP AUTH enabled can still use only OAuth.
2. Disable POP and IMAP in Exchange Online:
|
1 2 3 4 5 |
#Turn off for all existing mailboxes Get-CASMailbox -ResultSize Unlimited | Set-CASMailbox -PopEnabled $false -ImapEnabled $false #Turn off by default for new mailboxes (so they don't get POP and IMAP turned on by default): Get-CASMailboxPlan | Set-CASMailboxPlan -PopEnabled $false -ImapEnabled $false |
3. Restrict Exchange ActiveSync to Users Who Need Mobile Access: For users who don’t access email on mobile devices, disable ActiveSync:
|
1 |
Set-CASMailbox -Identity <MailboxUPN> -ActiveSyncEnabled $false |
Disable Exchange Web Services (EWS) in Exchange Online
Microsoft is retiring EWS in Exchange Online, with phased disablement beginning in October 2026 and completion planned for April 2027. Migrate EWS-dependent applications to Microsoft Graph or another suitable alternative.
Check the current EWS configuration and allowed application IDs:
|
1 2 |
Get-OrganizationConfig | Format-List EwsEnabled Get-OrganizationConfig -RetrieveEwsOperationAccessPolicy | Format-List EwsAllowedAppIDs |
If both values are blank, EWS hasn’t been configured and is currently allowed for all apps. Microsoft will change it to False during its rollout, unless you set it yourself.
To block EWS for the whole organization, run the cmdlet below. This applies to every mailbox, even those with EWS enabled at the mailbox level:
|
1 |
Set-OrganizationConfig -EwsEnabled $false |
Note: If both values are blank, EWS hasn’t been configured in your tenant and is currently allowed for all apps. Microsoft will change it to False during the phased rollout that began on October 1, 2026, unless you set it yourself.
Or, allow EWS only for specific apps, using their application IDs from the EWS usage report:
|
1 2 |
Set-OrganizationConfig -EwsEnabled $true Set-OrganizationConfig -EwsAllowedAppIDs "<AppId1>,<AppId2>" |
Block Legacy Authentication Using Conditional Access
Disabling Basic Authentication in Exchange Online addresses protocol-level settings. A Microsoft Entra Conditional Access policy adds another layer of protection by blocking legacy authentication attempts across your tenant.
Conditional Access requires a Microsoft Entra ID P1 or higher license. If you don’t have one, use security defaults to block legacy authentication. To create the policy:
- In the Microsoft Entra admin center, go to Entra ID → Conditional Access → Create new policy.
- Under Users, include All users and exclude your emergency access accounts.
- Under Target resources, select All resources.
- Under Conditions → Client apps, set Configure to Yes, and select Exchange ActiveSync clients and Other clients.
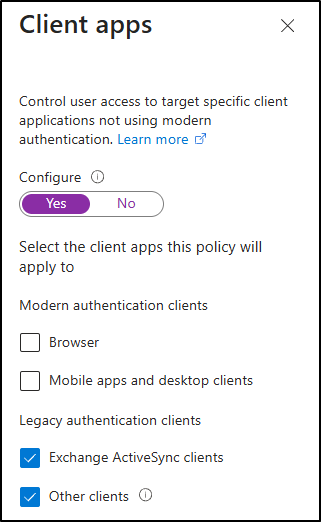
5. Under Grant, select Block access.
6. Set the policy to Report-only first, review the impact, and then turn it on.
Monitor Basic Authentication Sign-ins and Get Alerts with AdminDroid
Blocking basic auth isn’t a one-time task. Old devices, forgotten scripts, and attackers running password spray attacks will keep trying it! However, monitoring this in the Microsoft Entra admin center is hard to sustain:
- Sign-in logs are kept for only 7 to 30 days, depending on your license.
- You have to filter both the interactive and non-interactive tabs every time.
- There’s no built-in alert unless you send the logs to Azure Monitor.
AdminDroid simplifies this with a dedicated report on basic authentication sign-ins. The basic authentication report shows every sign-in made using basic auth, along with the signed-in user, application, sign-in status, and MFA status.
You can filter it by user, application, or protocol, and the summary chart shows successful and failed sign-ins at a glance. A spike in failures often signals a password spray attempt or an app with an outdated saved password.
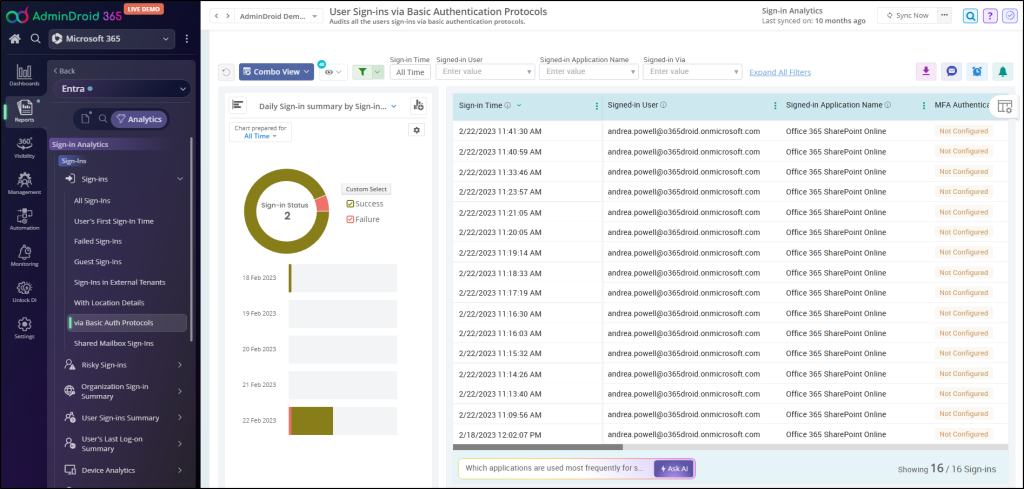
🔔You can also schedule this report to arrive in your inbox, and set alerts to be notified as soon as someone signs in using basic authentication!
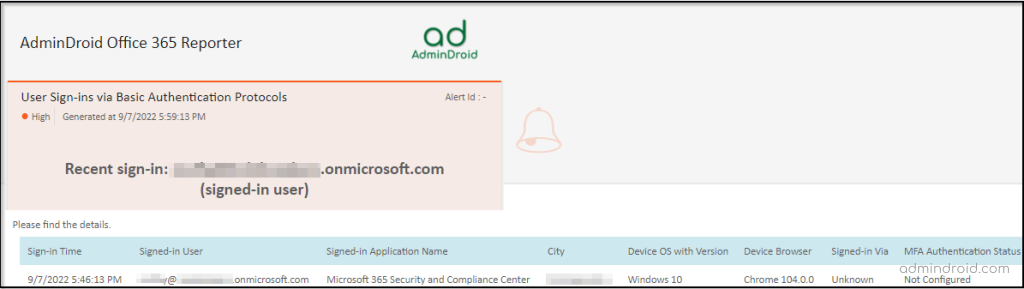
Beyond basic auth, AdminDroid gives you complete visibility into all Microsoft 365 user sign-ins, including risky, failed, and guest sign-ins, in a single place.
That brings us to the end of the guide! Basic authentication is almost gone from Exchange Online, but SMTP AUTH and EWS still need your attention before their deadlines at the end of December 2026 and April 1, 2027.
By finding what still relies on basic auth, moving it to modern authentication, and blocking what’s left, you can make sure nothing breaks when those changes arrive. Acting now gives you time to test each change, instead of fixing failed apps and devices after the deadline.
Stronger the Authentication! Safer the Organization!!